
Boost Retention 5–10 pts: AMS Insurance Renewal Reminders for Agencies
AMS first playbook for independent agencies: start 90 days out with email, SMS, and calls, respect TCPA, and aim for 5–10 point retention lift.

Yes, you need to register. If your business sends application-to-person SMS from a U.S. 10-digit long code, you must register a Brand and a Campaign with The Campaign Registry (TCR), and carriers now block unregistered traffic outright. A2P 10DLC compliance means clearing two separate hurdles: getting your Brand and Campaign approved, and satisfying the legal consent standards under the Telephone Consumer Protection Act (TCPA) that registration alone does not cover.
Here’s what to do right now:
A2P 10DLC compliance requires both a completed TCR Brand and Campaign registration and an independently defensible TCPA consent trail, since carrier approval alone does not satisfy federal or state consent law.
| Point | Details |
|---|---|
| Registration is non-negotiable | Carriers block unregistered 10DLC traffic entirely, with no grace period for late filers. |
| Two compliance layers exist | Carrier vetting controls deliverability; TCPA and state mini-TCPA laws control legal consent. |
| Rejections are usually avoidable | Name mismatches and vague campaign descriptions cause most denied applications. |
| Compliance is ongoing, not one-time | Quarterly audits of opt-in flow, STOP/HELP handling, and content categories keep trust scores healthy. |
| Upriser automates the audit trail | The platform captures consent metadata and handles STOP/HELP replies so records survive a TCPA challenge. |
Brand registration and Campaign registration are two distinct steps managed through TCR, and skipping the sequence or rushing either one is the fastest way to get bounced back. You register the Brand first, establishing your business identity, then register one or more Campaigns underneath it describing exactly how you’ll use the number.
TCR supports a few brand types, and picking the wrong one costs you time. Standard brands fit incorporated businesses with an EIN. Sole Proprietor brands exist for individuals or unregistered businesses without a formal EIN, though they come with lower throughput ceilings. Some providers also offer Low-Volume campaign paths for businesses sending under a few thousand messages a day, which face lighter vetting than standard mixed-use campaigns.
Whatever brand type you choose, TCR expects the same core fields:
Gather your EIN confirmation letter, your Secretary of State filing, or a business license before you start. If your legal name and website name don’t match exactly, add a “doing business as” note in your submission.
Pro Tip: Screenshot your actual opt-in form and keep it on file. Reviewers can request this evidence, and having it ready beats scrambling for it during a rejection appeal.
Carrier registration and federal consent law solve two different problems, and one does not substitute for the other. Registering your Brand and Campaign tells carriers who you are and what kind of traffic to expect, which affects deliverability and throughput. The TCPA governs whether you had legal permission to text someone at all, and it carries statutory damages that carrier approval does nothing to shield you from.
Several states layer their own “mini-TCPA” statutes on top of federal rules, sometimes with stricter consent windows or steeper penalties. Since you often can’t be certain where every recipient lives, the safer approach is applying the strictest applicable state standard across your whole list rather than segmenting by jurisdiction.
Carrier deliverability and legal compliance are complementary but distinct — a lesson the FCC’s own rulemaking makes clear when it separates blocking mechanics from consent obligations entirely.
TCR reviewers reject vague submissions more than almost anything else. Your sample messages need to mirror what you’ll actually send, including the exact opt-out language (“Reply STOP to unsubscribe”) and a clear sender identity. A campaign description like “we send updates to customers” gets flagged; “we send appointment confirmation texts to dental patients who booked online and opted in via our booking form checkbox” gets approved.
The most common rejection reasons repeat themselves across nearly every failed submission: EIN or legal name mismatches between your TCR filing and public business records, campaign descriptions too generic to categorize, and privacy policies that never mention texting at all.
Pro Tip: Before submitting, have someone unfamiliar with your business read your campaign description cold. If they can’t tell you exactly what kind of texts you send and why, TCR reviewers won’t either.
Approval timelines vary, and the honest answer is that most registrations clear within a couple of weeks, though verification snags, mismatched business details, or high-risk verticals can stretch that out. Expect a one-time brand vetting fee plus small per-message pass-through fees charged by carriers, which you should factor into your messaging budget rather than treat as an afterthought.
Enforcement has real teeth now. Since February 2025, major U.S. carriers have blocked unregistered A2P 10DLC traffic outright, meaning an unregistered number simply stops delivering, with no warning message and no fallback. That’s not a slowdown, it’s a wall.
Your trust score, assigned during vetting, determines your daily throughput cap. Higher-trust Standard brands with verified EINs and clean histories get meaningfully higher daily message allowances than unverified Sole Proprietor brands, which sit at the bottom of the throughput ladder. Low trust scores don’t just limit volume, they also make carriers more likely to flag your traffic for content review.
Treat this as a sequence, not a wish list. Each phase builds on the last, and skipping ahead usually means redoing work later.
| Point | Details |
|---|---|
| Registration is mandatory | Carriers block unregistered A2P traffic entirely since February 2025. |
| Two separate obligations | 10DLC controls deliverability; TCPA controls legal consent, and neither replaces the other. |
| Rejections are preventable | Vague campaign descriptions and name/EIN mismatches cause most denials. |
Manually tracking consent timestamps, STOP replies, and quarterly content audits across every channel is where most small teams lose the thread. A platform built for automated messaging can carry that weight instead of a spreadsheet.
Registration gets your number vetted. What keeps you compliant long after that is the audit trail nobody sees until they need it.
Registration is not a one-time filing you forget about. If your legal business name changes, you acquire another entity, or you add a new messaging use case, your TCR registration needs an update, not a brand-new submission from scratch in most cases.
Business detail changes, like a new EIN after incorporation, a legal name change, or a new registered address, require updating your Brand profile directly through TCR or your messaging provider’s portal. Carriers re-vet the updated information, and a mismatch between your old and new filings can trigger a temporary drop in trust score while the update processes, so plan ahead rather than switching entities mid-campaign.
Use-case changes are more common and easier to overlook. If you originally registered a Campaign for appointment reminders and later start sending promotional offers through the same number, that’s a use-case shift that technically falls outside your approved campaign description. Carriers and TCR both expect a new or amended Campaign registration reflecting the addition, and running mismatched traffic against your original filing risks throttling or suspension even if your Brand stays in good standing.
The safest practice is treating any material shift, new marketing push, new vertical, new consent flow, as a trigger for a registration review. Set a recurring calendar reminder, quarterly works well for most teams, to compare your live messaging content against what’s on file with TCR. If they’ve drifted apart, file the update before a carrier flags it for you. Waiting for a rejection or a throughput cut to notice the mismatch costs you both time and deliverability you can’t easily recover overnight.
Passing initial vetting is the easy part. Staying compliant means building habits that outlast the registration paperwork itself.
Set a recurring internal review, monthly or quarterly depending on your send volume, that checks four things: your opt-in flow still matches what’s on file, your STOP/HELP automation is still firing correctly, your sample messages on record still reflect what you actually send, and your consent logs are still capturing the metadata a TCPA claim would require. Consent logging that records timestamp, source URL, IP address, and the exact disclosure text shown is frequently the deciding factor when a dispute reaches discovery, and it’s far easier to build that habit now than to reconstruct it after a complaint arrives.
Watch your trust score the way you’d watch a credit score. A sudden drop usually signals something specific: rising opt-out rates, a spike in spam complaints, or carrier flags on content that drifted into a restricted SHAFT category without anyone noticing. Investigate drops immediately rather than waiting for throughput caps to tighten further.
Vendor due diligence matters more than most teams assume. If you use a third-party platform or agency to send on your behalf, confirm they maintain their own registered campaigns and don’t route your traffic through a shared, poorly vetted number. Shared infrastructure with bad actors drags down deliverability for everyone attached to it.
Finally, retain records. Consent logs, sample message archives, and registration correspondence should sit somewhere searchable for as long as your legal counsel advises, typically well beyond the life of any single campaign.
TCR sorts every campaign into a use-case category, and that category shapes both how closely you’re vetted and how many messages you can send per day. Marketing campaigns face the strictest vetting because they carry the highest consent risk and the highest complaint potential. One-time passcodes (OTP) get the lightest scrutiny and the highest throughput allowances, since they’re time-sensitive, low-risk, and rarely generate complaints. Customer care campaigns, covering appointment reminders, order updates, and support replies, land in between.
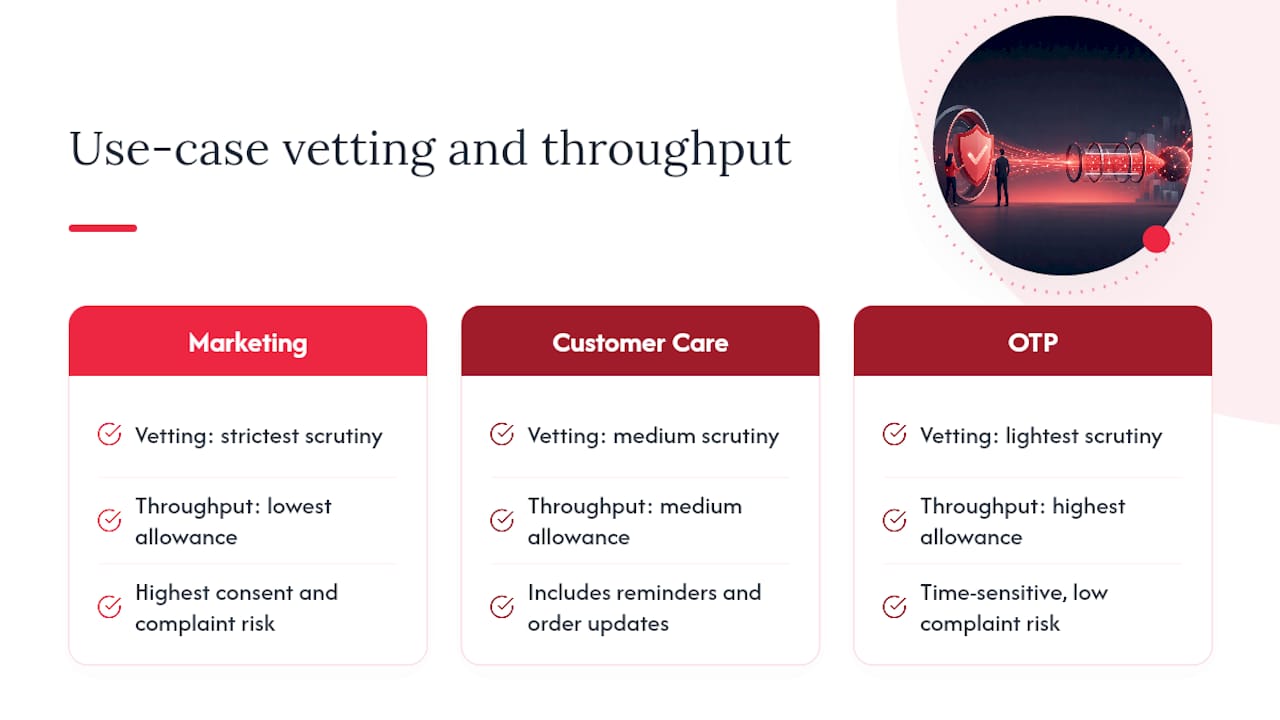
This categorization isn’t a formality. A marketing campaign registered under a low-scrutiny category like customer care will eventually get flagged when carriers notice the mismatch between declared use case and actual content, and that mismatch can trigger a registration review or a throughput cut. Register honestly for the category that matches your real traffic, even if it means slightly more paperwork upfront.
Mixed-use campaigns, where a single number sends both appointment reminders and occasional promotional offers, tend to get the most scrutiny of all, since they blur the line between two consent standards. If your business genuinely needs to send both transactional and marketing content, registering separate campaigns for each, ideally on separate numbers, keeps your throughput and trust score cleaner than trying to force both into one filing. It also keeps your legal consent trail simpler: a customer who opted into appointment reminders didn’t necessarily opt into marketing, and mixing the two under one registration muddies that distinction in a way that can matter if a complaint ever surfaces.
The gap between a compliant message and a rejected one often comes down to a handful of specific elements, not some vague sense of “professionalism.”
A compliant appointment reminder reads something like: “Hi Sarah, this is Riverside Dental confirming your cleaning on Tuesday at 2pm. Reply STOP to opt out, HELP for help.” It names the sender, states the purpose plainly, and includes the required opt-out language every single time, not just on the first message in a thread.
A non-compliant version might read: “Hey! Big news you don’t want to miss, tap here now!” with no sender identification, no opt-out instruction, and content vague enough that a carrier can’t tell if it’s marketing, a scam, or spam. Messages like this get flagged fast, both by carrier filters and by frustrated recipients who report them.
Content restrictions matter just as much as structure. Carriers enforce SHAFT category limits, meaning sex, hate, alcohol, firearms, and tobacco content, and messages touching any of those categories face outright blocking or require specialized high-risk vetting most standard campaigns don’t have. A gym registering a standard marketing campaign that later sends supplement promotions bordering on health claims risks a mismatch between registered content and actual sends.
Real estate texts offer a useful example of getting it right: a compliant showing confirmation template names the agent, references the specific property, and includes opt-out language, versus a generic “check out this listing!” blast that reads as unsolicited marketing to anyone who didn’t explicitly opt in to that agent’s texts.
Trust score and throughput cap are the same conversation from two different angles. A verified Standard brand with a clean complaint history, consistent content matching its registered campaign, and low opt-out rates earns a higher trust score, and that score translates directly into how many messages per day carriers will let through before throttling kicks in.
Low trust scores compound in ways that catch businesses off guard. A single spike in spam complaints, even from a small batch of poorly targeted messages, can drop your score enough to cut your daily send limit noticeably, and recovering that score takes weeks of clean sending, not a quick fix. Businesses that treat their trust score as a one-time approval rather than a running metric often discover the cap tightening right when they need volume most, during a seasonal promotion or a service disruption requiring mass outreach.
Quality scores factor in beyond raw complaint counts, too. Carriers track delivery success rates, how often recipients engage versus ignore or block, and whether your content stays consistent with what you registered. A campaign that drifts from “customer care” into occasional marketing sends, even accidentally, risks a quality downgrade that affects every message on that campaign, not just the drifting ones.
The practical takeaway: throughput isn’t a fixed number you negotiate once. It’s a live reflection of how clean your sending behavior stays over time, and the businesses with the highest sustained throughput are the ones treating compliance as an ongoing discipline rather than a registration checkbox.
If you were sending A2P SMS before 10DLC enforcement tightened, you likely have legacy traffic still running on unregistered or improperly categorized numbers. That traffic is now at direct risk of being blocked without warning.
Start by auditing every number your business currently uses to send SMS, including numbers set up years ago by a previous employee, agency, or platform that may not still exist. Confirm whether each number is registered, and if so, under what brand and campaign category. Numbers that predate your current registration process often carry outdated or missing campaign descriptions that no longer match what you’re actually sending.
Migrate legacy traffic in phases rather than all at once. Register the highest-volume or highest-priority number first, since that’s the one where a sudden block would cause the most disruption, then work through the rest. Run each migrated number through a brief test period, sending a small batch of real traffic and confirming delivery, before retiring the old unregistered version entirely.
Don’t assume a number that worked fine last year still will. Carrier blocking of unregistered traffic since February 2025 means legacy exemptions that may have existed earlier no longer apply. If you’re unsure whether a number needs migration, treat it as though it does. The cost of an unnecessary registration is small; the cost of a blocked customer notification system mid-migration is not.
Every A2P 10DLC campaign must honor opt-out requests immediately, and “immediately” has a specific meaning carriers enforce strictly: a single reply of STOP, UNSUBSCRIBE, CANCEL, END, or QUIT must trigger an automatic suppression of that number from all future sends, with no exceptions for message type.
The confirmation reply matters too. After a recipient opts out, industry practice expects a brief confirmation text, something like “You’ve been unsubscribed and won’t receive further messages. Reply START to resubscribe,” sent once and only once. Continuing to send any message after a STOP request, even an unrelated transactional one, is a direct compliance failure that can trigger both carrier penalties and a TCPA complaint.
HELP requests carry a different obligation. A HELP reply should trigger an automatic response with your business name, a brief description of the message program, and a support contact method, typically a phone number or email. Unlike STOP, a HELP request doesn’t suppress future messages, it just needs a timely, informative response.
Timing windows matter for both. Carriers generally expect STOP and HELP auto-responses to fire within seconds, not hours, since a delayed opt-out confirmation looks identical to a business ignoring the request altogether. If your messaging platform can’t confirm STOP suppression happened before the next scheduled send, you’re running a real compliance gap regardless of your registration status. Two-way texting workflows built around instant STOP/HELP recognition close that gap far more reliably than a manual suppression list someone updates once a week.
The pitfall I see most often isn’t a rejected registration. It’s teams that pass registration cleanly, then never touch their opt-in wording or consent logging again, assuming the hard part is done. It isn’t.
If you’re a small team with limited hours, fix your opt-in disclosure and start logging consent metadata before you even submit to TCR. Registration approval means nothing legally if your underlying consent trail can’t survive a TCPA complaint.
Registration paperwork is only half the job. The harder half, keeping consent records airtight, catching STOP requests instantly, and making sure your sample messages still match what you actually send six months later, is where most businesses quietly fall behind.

Upriser handles that ongoing half automatically. Instead of stitching together a spreadsheet for consent logs and a separate tool for STOP/HELP replies, Upriser’s platform builds the audit trail into your messaging workflow from the first opt-in:
Property services, hospitality, and dental practices already run their customer messaging through Upriser’s unified communication platform for exactly this reason: compliance stops being a quarterly scramble and becomes something the system handles by default. If you’re managing a property portfolio, see how Upriser’s property services tools handle tenant and vendor messaging with the same built-in compliance logic, and get a walkthrough of what your specific setup would need.
Is A2P 10DLC registration legally required, or just recommended by carriers?
It’s effectively mandatory for functional messaging. Carriers have blocked unregistered A2P traffic outright since February 2025, so while no federal statute forces registration, sending without it means your messages simply won’t deliver.
Does completing 10DLC registration mean I’m automatically TCPA compliant?
No. Registration confirms carriers know who you are and what you send; it says nothing about whether you had valid consent to text each recipient, which is a separate legal standard under the TCPA.
How long does A2P 10DLC registration typically take?
Most clean submissions clear within a couple of weeks, though mismatched business details or unclear campaign descriptions can push approval out considerably longer.
What’s the difference between Standard and Sole Proprietor brand registration?
Standard brands require an EIN and fit incorporated businesses, with higher throughput allowances. Sole Proprietor brands suit individuals or unregistered businesses without an EIN, but carry lower daily message caps.
Can I use the same registered campaign for both marketing and appointment reminders?
It’s risky. Mixed-use campaigns blur consent standards and use-case categories, and carriers may flag the mismatch, so registering separate campaigns for marketing versus transactional content keeps your trust score cleaner.
What happens if a customer texts STOP and I accidentally send another message?
That’s a direct compliance failure that can trigger both carrier penalties and a potential TCPA complaint, since suppression after STOP must apply immediately and across all future sends, regardless of message type.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.


